A developer on a client’s team opened two terminal tabs, one for staging and one for production. He meant to clean up an old test copy, typed the command in the wrong tab, and pressed Enter. Within a second, a production database with eight months of order history was gone. The team had backups, but nobody had ever tested a restore, so the next six hours were stressful.
That story is why I treat drop database psql commands with respect. DROP DATABASE is fast, permanent, and has no recycle bin. The command is simple, but the process around it decides whether you have a calm cleanup or a very bad weekend.
In this guide, you will learn the exact syntax, how to handle active connections, how to drop databases on Azure Database for PostgreSQL Flexible Server, how to build a safe process with backups and approvals, and how to fix the errors that block you.
Drop Database PSQL
What DROP DATABASE Actually Does
A PostgreSQL database is an isolated container with its own schemas, tables, indexes, and extensions. DROP DATABASE removes the catalog entry and deletes all the files on disk that belong to it. Everything inside is gone: tables, views, functions, and data. For background on how databases fit into the server, read about PostgreSQL architecture.
Key rules to know before you run it:
- You must be the owner of the database or a superuser. On Azure Flexible Server, the admin role belongs to the
azure_pg_admingroup instead of a true superuser. - You cannot drop the database you are connected to. Connect to
postgresor another database first. - It cannot run inside a transaction block. There is no
ROLLBACKthat undoes it. - Other sessions must disconnect unless you use the
FORCEoption, which PostgreSQL 13 and later support.
It also does not touch cluster-wide objects. Roles (users) belong to the whole server, so dropping a database does not remove the roles that used it. If you need that cleanup, see how to delete a user in PostgreSQL.
Pro Tip: In my experience, I treat
DROP DATABASElike a production deployment. It gets a ticket, a second pair of eyes, and a named backup before anyone types it.
Check Where You Are Before You Type Anything
The most common disaster is not a bad command, it is the right command on the wrong server. Build the habit of verifying your target first.
Connect securely with TLS enforced:
psql "host=<server-name>.postgres.database.azure.com port=5432 dbname=postgres user=<admin-user> sslmode=require"This opens psql on the postgres maintenance database. host is the server address. sslmode=require forces an encrypted connection and fails if TLS is not available. If you are new to connecting, follow this guide on how to connect to a PostgreSQL database, and if the server will not answer, see could not connect to PostgreSQL server.
Now confirm the server, user, and database list:
SELECT current_user,
       inet_server_addr() AS server_ip,
       current_database(),
       version();
This returns your role, the server’s address, the current database, and the PostgreSQL version. Compare it against what you expect for the target environment. On Azure, the address may be a private IP if you use private access.
Then list databases with sizes and owners:
SELECT d.datname AS database_name,
       pg_get_userbyid(d.datdba) AS owner,
       pg_size_pretty(pg_database_size(d.datname)) AS size,
       d.datallowconn AS allows_connections
FROM   pg_database AS d
WHERE  d.datistemplate = false
ORDER  BY pg_database_size(d.datname) DESC;
pg_database_size returns bytes, and pg_size_pretty formats them. A “test” database that is 400 GB is not a test database. To see more listing methods, read how to list databases in PostgreSQL.
A trick I use: set a loud psql prompt for production sessions. Add \set PROMPT1 '%n@%M:%> [%/]%R%# ' to your session so the host and database name show on every line. Wrong-tab mistakes become much harder to make.
Pro Tip: I color production terminal tabs red. It sounds silly, but it has stopped real mistakes more than any policy document I have written.
The Basic DROP DATABASE Syntax
Here is the standard form, run from a different database such as postgres:
DROP DATABASE IF EXISTS orders_test_2026;After running the above query, I got the expected output as shown in the screenshot below.
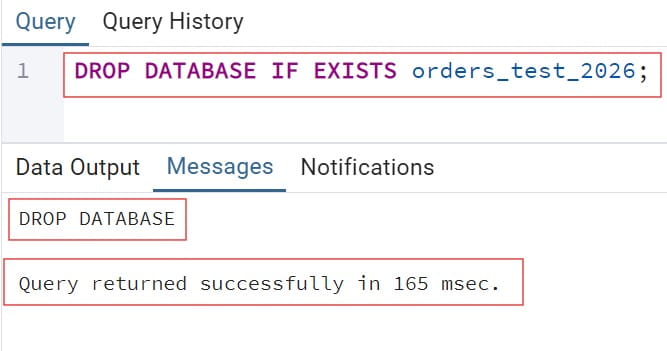
This deletes the database named orders_test_2025 if it exists. IF EXISTS turns a “does not exist” error into a harmless notice, which is useful in scripts. Without it, a typo or a repeated run causes an error and stops your script.
You can also use the command-line tool dropdb, which wraps the same SQL:
dropdb \
  --host=<server-name>.postgres.database.azure.com \
  --username=<admin-user> \
  --interactive \
  --if-exists \
  orders_test_2026
--host and --username select the server and role. --interactive makes the tool ask for confirmation before it deletes, which gives you one last chance to cancel. --if-exists avoids an error if the database is already gone. The dropdb tool reads your password from the PGPASSWORD variable or a .pgpass file, so do not put passwords in the command line where shell history can store them.
If you need a refresher on the creation side, see how to create a database in PostgreSQL.
Pro Tip: I always use
--interactivein manual sessions and never in scripts. Humans need the pause, and automation needs a different safety mechanism, which I cover later.
Handle Active Connections and the “Being Accessed” Error
The most common error looks like this:
ERROR:  database "orders_test_2026" is being accessed by other users
DETAIL:  There are 3 other sessions using the database.
PostgreSQL refuses to drop a database that has active sessions. A session is one client connection. First, see who is connected:
SELECT pid,
       usename,
       application_name,
       client_addr,
       state,
       query_start
FROM   pg_stat_activity
WHERE  datname = 'orders_test_2026'
  AND  pid <> pg_backend_pid();
After running the above query, I got the expected output as shown in the screenshot below.
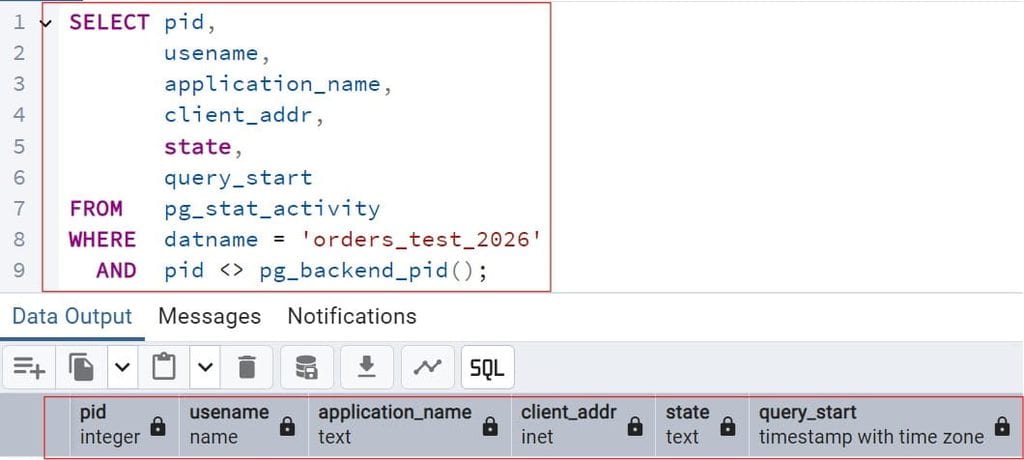
This reads the pg_stat_activity view, which lists current sessions. pg_backend_pid() is your own session, so the filter excludes you. Look at application_name and client_addr before you terminate anything, because an app server you forgot about may be holding those connections.
Use DROP DATABASE WITH (FORCE)
On PostgreSQL 13 and later, FORCE terminates other connections for you:
DROP DATABASE orders_test_2026 WITH (FORCE);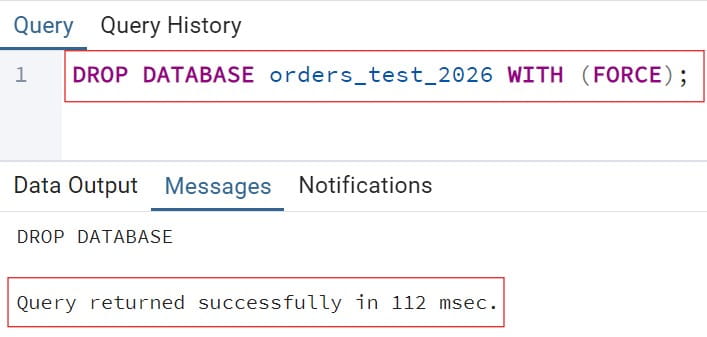
PostgreSQL first tries to terminate all other sessions, then drops the database. If it cannot terminate a session, for example because your role lacks permission, the command fails. This is the simplest path, but it is also the most dangerous one, since it kills connections without any warning to the apps using them.
Block new connections first
An application with a retry loop may reconnect between your terminate command and your drop. Close the door first:
REVOKE CONNECT ON DATABASE orders_test_2026 FROM PUBLIC;
ALTER DATABASE orders_test_2026 WITH ALLOW_CONNECTIONS false;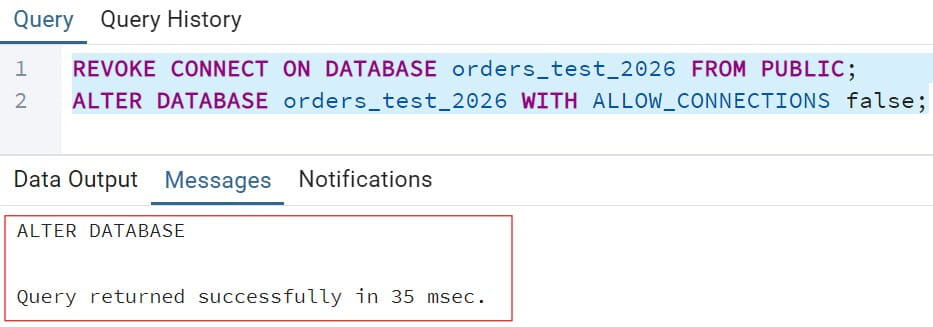
The first statement removes the default right to connect from every role. The second marks the database as closed to new connections for everyone, including roles with explicit grants. Then terminate existing sessions:
SELECT pg_terminate_backend(pid)
FROM   pg_stat_activity
WHERE  datname = 'orders_test_2026'
  AND  pid <> pg_backend_pid();
pg_terminate_backend ends each session. On Azure Flexible Server, you need membership in azure_pg_admin or the pg_signal_backend role for this. Once the sessions are gone, run a plain DROP DATABASE.
Pro Tip: I once watched a connection pool reconnect 40 times in ten seconds during a drop. Closing the database to new connections first took the drama out of it.
A Safer Process: Back Up, Rename, Wait, Drop
Here is the workflow I use in production, in order. Each step costs little and removes a type of regret.
Step 1: Take a logical backup
A logical backup exports the database as SQL or an archive using pg_dump. It is portable and lets you restore one database without touching the others.
pg_dump \
  --host=<server-name>.postgres.database.azure.com \
  --username=<admin-user> \
  --dbname=orders_test_2025 \
  --format=custom \
  --file=orders_test_2025_$(date +%Y%m%d).dump
--format=custom creates a compressed archive that pg_restore can read selectively. --file names the output. The $(date +%Y%m%d) part appends today’s date so you can tell dumps apart. Store the file in a protected location, such as a private storage container with restricted access, not a shared drive. For more options, see how to back up a PostgreSQL database.
Then prove the dump works by restoring it into a scratch database:
createdb --host=<server-name>.postgres.database.azure.com --username=<admin-user> restore_check
pg_restore \
  --host=<server-name>.postgres.database.azure.com \
  --username=<admin-user> \
  --dbname=restore_check \
  orders_test_2025_20261009.dump
createdb makes an empty database and pg_restore loads the archive into it. If the restore succeeds, check a few row counts. A backup you have not restored is only an assumption.
Step 2: Rename instead of drop
Renaming gives you a reversible “soft delete”:
ALTER DATABASE orders_test_2025
  RENAME TO orders_test_2025_pending_drop_20261009;

ALTER DATABASE orders_test_2025_pending_drop_20261009
  WITH ALLOW_CONNECTIONS false;
The rename changes the name apps use, so any app that still depends on the database fails loudly right away. If someone screams, you can rename it back in seconds. You must have no active sessions on the database to rename it.
Step 3: Wait, then drop
Wait a defined period, such as seven days for test databases and thirty for anything that ever held customer data. After the wait, drop it:
DROP DATABASE orders_test_2026_pending_drop_20261009;The long name is a feature. It forces you to type the full target, which makes accidental drops less likely than using a short name like orders.
Pro Tip: I put the drop date in the renamed database’s name. When the cost review asks why a database still exists, the name itself answers.
Drop a Database on Azure Database for PostgreSQL
For Azure Database for PostgreSQL Flexible Server, the same SQL works, and the Azure CLI gives you a control-plane option. New deployments should use Flexible Server, and this comparison of Single Server vs. Flexible Server explains why. Sign in first with Azure CLI login.
az postgres flexible-server db delete \
  --resource-group <resource-group-name> \
  --server-name <server-name> \
  --database-name orders_test_2026 \
  --yes
This deletes one database on the server through Azure Resource Manager, the deployment and management layer for Azure. --yes skips the confirmation prompt, so only use it in automation that has its own approval step. The caller needs an Azure RBAC role with permission to write to the server resource. Read what RBAC is to design roles that give people read access without delete rights.
Be careful with a few Azure details:
- System databases: You may see databases like
azure_maintenanceandazure_systhat Azure manages. Never drop them. - Resource locks do not protect databases. A
CanNotDeletelock on the server or resource group prevents someone from deleting the Azure resource, but it does not blockDROP DATABASEinside the server, because that is a data-plane operation. Protect databases with roles and process. - Tagging helps ownership. Use consistent Azure tags on servers so you can find who owns a database before you remove it.
Keep servers in a dedicated group, as covered in how to create a resource group in Azure, so access reviews stay simple.
Pro Tip: I explain the lock gap in every Azure database training. People assume a delete lock protects their data, and it only protects the server object.
Recover After a Mistaken Drop
If the wrong database is dropped, your recovery options depend on what you prepared.
Logical dump. If you took a pg_dump, create a new database and restore the dump. This is the fastest and cleanest path for a single database.
Point-in-time restore (PITR). Azure Flexible Server keeps automated backups for a retention period you set, from 7 to 35 days. PITR restores the entire server to a chosen moment into a new server. It does not restore one database in place. The recovery steps are:
- Note the time just before the drop.
- Restore the server to that time as a new server.
- Connect to the new server, and
pg_dumpthe missing database. - Restore that dump into the original server.
- Delete the temporary server to stop its cost.
az postgres flexible-server restore \
  --resource-group <resource-group-name> \
  --name <restored-server-name> \
  --source-server <server-name> \
  --restore-time "2026-10-09T08:15:00Z"
--source-server names the server to restore from, and --restore-time is the UTC time to roll back to. The restored server is billed while it exists, so remove it after you copy out your data. Retention settings and region availability vary, so check your server’s configuration. High availability replicas do not help here, because a dropped database drops on the standby too.
Self-managed servers. You need base backups plus archived WAL files. WAL is the write-ahead log, a sequential record of every change that lets PostgreSQL replay activity after a base backup. Without archived WAL, you can only restore to the time of the last full backup.
If you dropped a whole Azure resource group by mistake, the story is different. See this guide to recover a deleted resource group for what is and is not possible.
Pro Tip: I schedule a PITR drill every quarter. Restoring to a scratch server and timing it gives me a real recovery time to show the business, instead of a guess.
Lock Down Who Can Drop Databases
Least privilege prevents most accidents before they start. Application roles should never own databases or hold the rights to drop them.
Use separate roles:
- Admin role: A small group of people who can create and drop databases, protected by MFA.
- Migration role: Changes schemas but cannot drop databases.
- Application role: Reads and writes data only.
- Reporting role: Read-only.
CREATE ROLE app_orders_rw LOGIN;
GRANT CONNECT ON DATABASE orders TO app_orders_rw;
GRANT USAGE ON SCHEMA public TO app_orders_rw;
GRANT SELECT, INSERT, UPDATE, DELETE ON ALL TABLES IN SCHEMA public TO app_orders_rw;
The role can connect and change rows, but it does not own the database and cannot drop it. Learn how objects are grouped in this overview of the PostgreSQL schema. To avoid stored passwords, use Microsoft Entra ID authentication on Flexible Server, along with managed identities for apps. Read what a managed identity in Azure is.
If you must keep any secret, store it in Azure Key Vault and follow these Azure Key Vault best practices. Test with a non-administrator role: log in as the app role and confirm that DROP DATABASE fails with a permission error.
For network exposure, use private access on a virtual network, so the server has no public endpoint. Review what an Azure virtual network is, and restrict port 5432 with a network security group. A private endpoint is another option for supported services. Never allow the entire internet range 0.0.0.0 to 255.255.255.255 in a firewall rule.
Enable pgaudit, a PostgreSQL extension that logs sensitive statements, and add ddl to its logging classes so DROP DATABASE appears in the logs. Send diagnostic logs to Azure Monitor and alert on those events. See what Azure Monitor does to plan alerts.
Pro Tip: I add an alert that emails the team whenever pgaudit logs a DROP statement on production. Nobody has dropped something quietly since.
Automate Drops With an Approval Gate
Automation is useful for cleaning up short-lived test databases, but it needs a gate. In Azure DevOps, you can attach an approval to an environment, so a pipeline stage pauses until a named person approves it.
texttrigger: none

parameters:
  - name: databaseName
    type: string

stages:
  - stage: DropDatabase
    jobs:
      - deployment: drop_db
        environment: postgres-prod-approvals
        pool:
          vmImage: ubuntu-latest
        strategy:
          runOnce:
            deploy:
              steps:
                - task: AzureCLI@2
                  inputs:
                    azureSubscription: '<service-connection-name>'
                    scriptType: bash
                    scriptLocation: inlineScript
                    inlineScript: |
                      az postgres flexible-server db delete \
                        --resource-group "$(resourceGroupName)" \
                        --server-name "$(serverName)" \
                        --database-name "${{ parameters.databaseName }}" \
                        --yes
The deployment job targets an environment named postgres-prod-approvals. You configure approvers on that environment, so the job waits for a human to approve. The database name is a runtime parameter, and server details come from pipeline variables, not hardcoded values. The service connection should use a scoped identity with only the rights it needs, not a subscription owner.
Add a validation step that refuses to run if the database name matches a protected list. Validate inputs strictly, because a pipeline parameter is user input. In Python, avoid string formatting when you build SQL:
pythonimport psycopg
from psycopg import sql

def drop_database(conn_info: dict, db_name: str) -> None:
    with psycopg.connect(**conn_info, autocommit=True) as conn:
        conn.execute(
            sql.SQL("DROP DATABASE IF EXISTS {} WITH (FORCE)").format(sql.Identifier(db_name))
        )
autocommit=True is required because DROP DATABASE cannot run in a transaction. sql.Identifier quotes the name safely, which prevents injection through the database name. Pass connection details from a token or Key Vault, never from source code.
Pro Tip: I make cleanup pipelines drop only databases whose names start with a known test prefix. A prefix check is a cheap guard against a pipeline pointed at the wrong target.
Cost Considerations When Removing Databases
Removing unused databases does help cost, but not always the way people expect. On Flexible Server, you pay for compute and provisioned storage at the server level. Dropping a database frees space inside the server, but the provisioned storage size does not shrink automatically, and Azure does not allow you to reduce it. Plan your sizing with that in mind.
The savings come from avoiding growth: smaller backups, less storage added, and less vacuum work. For real savings, move small, idle databases onto fewer servers, or stop non-production servers when idle. Use budgets, cost analysis, and Azure Advisor to spot oversized servers, and set budget alerts so surprises reach you early. Follow Azure Policy best practices if you want tagging and private-access rules enforced across teams.
After a large drop, run maintenance on the remaining databases. Learn the difference between VACUUM and VACUUM FULL before you reach for the heavier option, since VACUUM FULL locks tables.
Pro Tip: I log the freed storage in the cleanup ticket. Teams like seeing a number, and it makes the next cleanup easier to approve.
Troubleshooting Common DROP DATABASE Errors
“database is being accessed by other users.” Sessions are still connected. Inspect pg_stat_activity, close the database to new connections, terminate sessions, or use WITH (FORCE) on version 13 or later.
“cannot drop the currently open database.” You are connected to the database you want to remove. Switch with \c postgres, then run the drop.
“DROP DATABASE cannot run inside a transaction block.” You used BEGIN or a client with autocommit off. Turn autocommit on, or run it as a plain statement.
“must be owner of database.” Your role does not own it. Ask the owner, or use an admin role that can take ownership.
“database is used by an active logical replication slot.” A replication slot is bound to the database. Drop the slot first with SELECT pg_drop_replication_slot('<slot-name>');, after confirming that no subscriber needs it.
“permission denied to terminate process.” Your role lacks the right to end other sessions. On Azure, use an admin role that belongs to azure_pg_admin.
Authentication problems. If your login fails before you reach the command, read this fix for password authentication failed, or check that your Entra token has not expired.
Pro Tip: When a drop fails, I read the DETAIL line before anything else. PostgreSQL usually tells you exactly how many sessions or which slot is in the way.
PostgreSQL Production Readiness Checklist
- Verified target: Confirm host, database name, and environment with a query before you run any drop, and use a visible prompt for production sessions.
- Tested backup: Take a
pg_dump, restore it into a scratch database, and check row counts before you delete anything. - Soft delete first: Rename the database with a pending-drop date, block connections, wait the agreed period, and then drop it.
- Least privilege: Keep application roles off ownership, use Entra ID and managed identities, and test that app roles cannot drop databases.
- Audit and alerts: Enable pgaudit with DDL logging, send logs to Azure Monitor, and alert on DROP statements in production.
- Recovery drill: Set PITR retention to match your needs, and rehearse a restore to a new server each quarter.
Frequently Asked Questions
How do I drop a database in psql?
Connect to a different database, such as postgres, and run DROP DATABASE IF EXISTS <database-name>;. You must own the database or have admin rights. Make sure no other sessions are connected, or use WITH (FORCE) on PostgreSQL 13 and later.
How do I force drop a PostgreSQL database with active connections?
Use DROP DATABASE <database-name> WITH (FORCE); on version 13 or later. On older versions, block new connections, run pg_terminate_backend for each session, and then drop the database. Check who is connected first so you do not break a live application.
Can I undo DROP DATABASE in PostgreSQL?
No, it cannot be rolled back. You can recover only from a backup, such as a pg_dump file or a point-in-time restore. On Azure, PITR restores the whole server to a new server, so you then copy the missing database back.
Why does DROP DATABASE fail with “being accessed by other users”?
Other sessions are still connected to that database. Find them in pg_stat_activity, stop the apps or terminate the sessions, and retry. Close the database to new connections first so applications cannot reconnect.
How do I drop a database in Azure Database for PostgreSQL?
Connect with an admin role and run DROP DATABASE, or use az postgres flexible-server db delete with the resource group, server name, and database name. Take a backup first, because a resource lock on the server does not stop a database drop.
You learned the exact DROP DATABASE syntax, how to handle active sessions, how to run a safe back-up-rename-wait-drop process, and how to recover on Azure with logical dumps and point-in-time restore. Never delete a database until you have restored a backup of it successfully, because a drop cannot be undone. I hope you found this article helpful.
You May Also Like
- PostgreSQL drop table command
- How to drop all tables in PostgreSQL
- How to restart PostgreSQL
- How to check the PostgreSQL version
- PostgreSQL create user with password
Kumar Saurabh is a freelance software engineer who builds web and mobile apps with Next.js, React, Flutter and Python. From 2021 to 2024, Saurabh worked as an IT analyst and developer at TSInfo Technologies, writing technical articles on SQL and PostgreSQL. Saurabh writes the PostgreSQL, MySQL, MariaDB and MongoDB tutorials on DatabaseFAQs.com and holds a Master of Computer Applications (MCA) from Chandigarh University.